Conformity Credential
Please note that this specification is suitable for pre-production pilot implementations.
Artifacts
v0.8.0 Schema, Context and Samples
The JSON schema, JSON-LD context and sample credential instances for the Conformity Credential are maintained in this repository. The v0.8.0 artefacts are the working version, a candidate for UNTP v1.0.0.
- JSON Schema:
| Schema | Description |
|---|---|
| ConformityCredential.json | Full credential schema including the W3C VC envelope and ConformityAttestation subject |
| ConformityAttestation.json | Standalone schema for the ConformityAttestation credential subject |
- JSON-LD Context:
| Context | Description |
|---|---|
| untp-context.jsonld | The shared UNTP JSON-LD context that binds the credential's terms to the UN/CEFACT vocabulary |
Vocabulary and Context
The Conformity Credential is built on the UNTP Core Vocabulary, which defines the shared classes and properties used across all UNTP credential types. The machine-readable vocabulary and JSON-LD context files are published under https://vocabulary.uncefact.org/untp/.
A credential references the versioned context, not that base path. For this release that is https://vocabulary.uncefact.org/untp/0.8.0/context/, which is what the samples on this page use. The unversioned path is where the vocabulary is published, not a context a credential can resolve.
Sample Credential
A live, signed sample Conformity Credential for v0.8.0 — with a QR code and a link to a hosted verifier that renders a human-readable version — is coming soon.
The static sample credential instance for the Conformity Credential is:
| Sample | Description |
|---|---|
| ConformityCredential_cathode_scheme_instance.json | Conformity attestation for cathode production (fictional SCSA scheme, scheme-derived) |
Scheme-derived assurance is the most common pathway in the sustainability space. Each component of the Conformity Credential is illustrated inline below with JSON-LD snippets; the sample above shows a complete worked instance.
Overview
A product passport typically makes various separate claims (eg emissions intensity, deforestation free, fair work, etc), each of which MAY be linked to a specific conformity credential. As well as providing details of assessment standards used to substantiate a claim, the conformity credential MAY also reference an assurance credential that attests to the authority of the party to perform the specific assessments.
Conformity assessment bodies (CABs) undertake assessments for the purpose of determining whether products, processes or organisations meet specified requirements. The joint UNIDO/ISO publication Building Trust - The Conformity Assessment Toolbox represents a useful resource for understanding conformity assessment and its role in international trade.
The conformity credential data model was originally developed by a separate UN/CEFACT project on digital conformity.
Conceptual Model
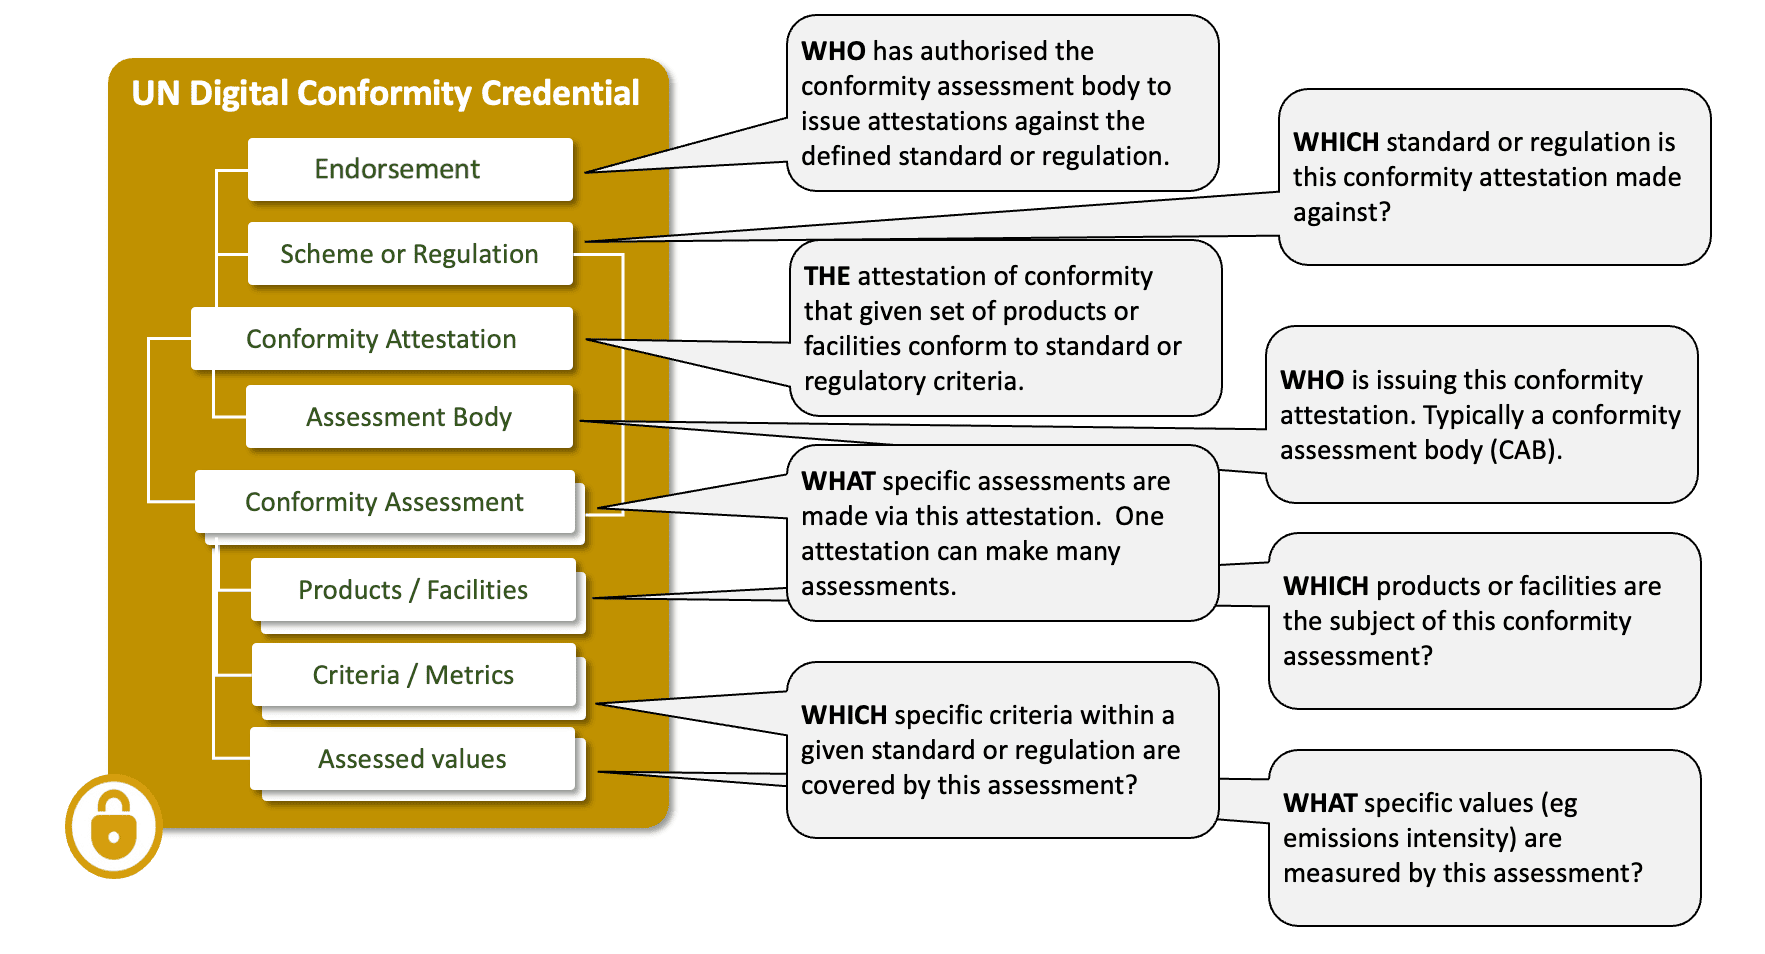
Design Requirements
The conformity credential is designed to meet the following detailed requirements as well as the more general UNTP Requirements.
| ID | Name | Requirement Statement | Solution Mapping |
|---|---|---|---|
| 01 | Signed | The issuer of the Conformity Credential, typically a conformity assessment body (CAB), MUST be verifiable | Conformity Credential MUST be issued as a digital verifiable credential signed by the CAB |
| 02 | Trust signals | The Conformity Credential MUST identify the nature of the evidence selection, assessor independence and assessment assurance. | ConformityAttestation.assessorLevel, ConformityAttestation.assessmentLevel, ConformityAttestation.evidenceSelection; ConformityAttestation.authorityEndorsement |
| 03 | Object of conformity | The Conformity Credential MUST unambiguously identify the object of the conformity assessment, whether a product, facility or organisation. | ConformityAssessment.assessedProduct, ConformityAssessment.assessedFacility, ConformityAssessment.assessedOrganisation |
| 04 | Assessment criteria | The Conformity Credential MUST identify the criteria against which the conformity assessment is made. If appropriate this SHOULD include specific measurable thresholds (eg minimum tensile strength). | ConformityAssessment.assessmentCriteria |
| 05 | Assessed performance | The Conformity Credential MUST unambiguously state the assessed performance against the assessment criteria, which MAY include actual measured values (eg emissions intensity, tensile strength, etc) | ConformityAssessment.assessedPerformance |
| 06 | Attestation coverage | The Conformity Credential MAY describe the coverage of the attestation in terms of scheme identity, geographical coverage or other elements | ConformityAttestation.coverage |
| 07 | Evidence | The Conformity Credential MAY include references to audit-able evidence (eg instrument recordings, satellite images, etc) to support the assessment. If so then the hash of the evidence file-set SHOULD be included (so that an auditor can be sure that the evidence data has not changed). The evidence data MAY be encrypted with decryption keys provided on request | ConformityAttestation.auditableEvidence |
Logical Model
The Conformity Credential is an assembly of re-usable components from the UNTP core vocabulary. The diagram below shows the Conformity Attestation — the credential subject carried inside the credential envelope — and the components it composes.
The conformity attestation may be understood as the nearest analogue to a traditional "paper" certificate. A copy of the traditional certificate issued by the conformity assessment body MAY be linked from the digital attestation, since not every detail of the traditional certificate will be digitally represented. The surrounding W3C Verifiable Credential envelope (issuer, validity, status, rendering) is omitted here for clarity; it is shown in full under Credential Schema.
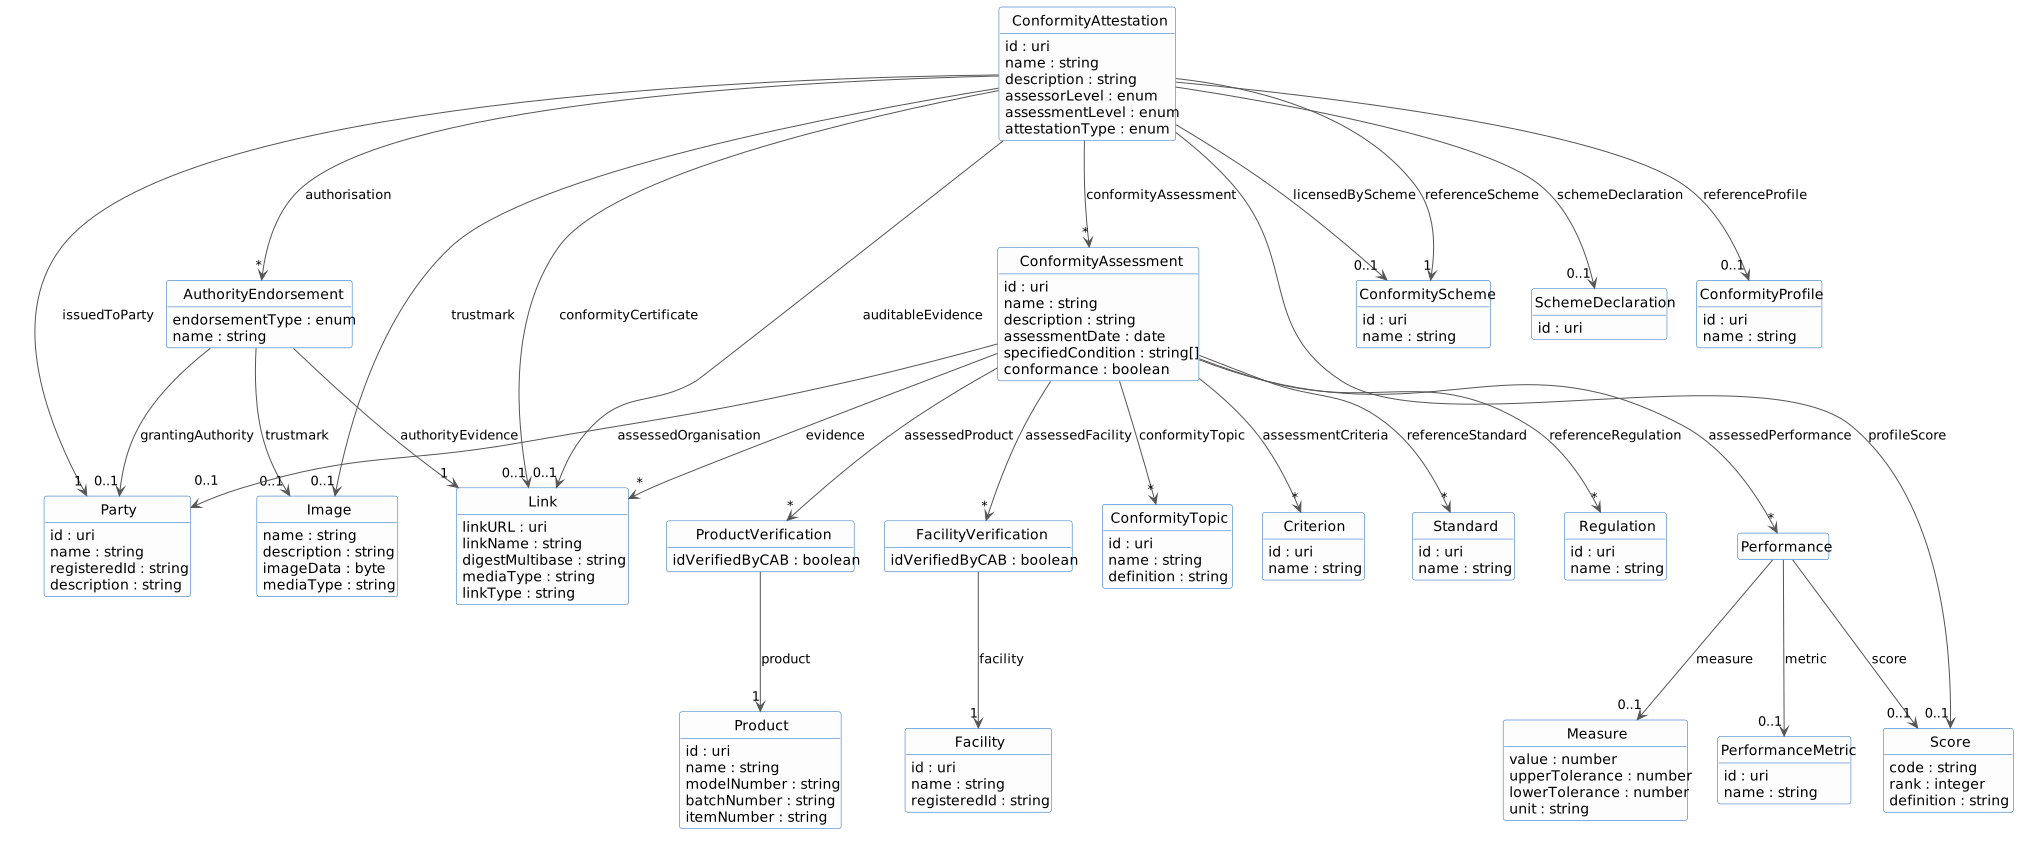
Read it top-down. The ConformityAttestation (top left) declares what it covers and carries one or more ConformityAssessment entries. Each assessment is made about a product, facility or organisation, against one or more Criterion, and records the outcome in assessedPerformance, where each entry states a metric and the result reached against it. Each box is an object; each labelled arrow is a property, with its cardinality (1, 0..1, *) shown at the target end. Enumerated code values (for example assessmentLevel) appear as enum and are defined in the Core Vocabulary.
For detailed class and property definitions, see the Core Vocabulary reference. Conformity topic and performance metric classifications are published as the conformity topics and performance metrics schemes, and Claims and Assessments covers how to apply them. For implementation details and sample JSON-LD snippets, see The Components of a Conformity Credential below.
Credential Schema
The full JSON Schema for the credential — the W3C Verifiable Credential envelope wrapping the Conformity Attestation subject — is the working version, a candidate for UNTP v1.0.0.
Assessment Assurance
Formal processes for substantiating claims made about products, processes or services represent a fundamental concept within UNECE Recommendation No.49 and within UNTP. However, for such processes to be reliable, it is essential to define the basis for confidence in such processes.
The UNTP approach embraces the objectives and design principles of UNECE Recommendation No. 49, by emphasising the concepts of verifiability, impartiality, international standards and the role of recognised authorities.
In this context, three categories of assurance have been defined, as follows.
| Assurance Category | Description |
|---|---|
| Authority-derived assurance | Assurance is available via one of the listed pathways that assessment credibility has been established and maintained in alignment with the objectives and design principles of UECE Rec. 49 and international conformity norms. |
| Scheme-derived assurance | Care is recommended as credibility derives from assurances provided by the referenced scheme, which do not necessarily represent suitable assurance that assessment credibility has been established in alignment with the objectives and design principles of UNECE Rec. 49 and international conformity norms. |
| No UNTP-recognised assurance | Available assurances are not recognised as representing suitable assurance that assessment credibility has been established in alignment with the objectives and design principles of UNECE Rec. 49 and international conformity norms. |
Describing assurance over the conformity assessment chain of results necessarily requires consideration of both the CAB processes and the scheme (or program) under which the assessment is delivered. However, assurance over a scheme and assurance over the conformity assessment processes (relating to that scheme) are sometimes established by different processes and by different parties and it is the combination of these that provides a more complete understanding of assessment assurance.
Defined assessment assurance levels are summarised below. Note that these relate to assurances over processes (including scheme-defined processes) implemented by CABs. They do NOT relate to assurances asserted in relation to a product, facility or organisation being assessed.
Eligibility for a given assessment assurance level is digitally verifiable through data points linked to a conformity credential and/or scheme representation. Any recognitions indicated MUST be maintained as current, with currency defined by the party providing such recognition.
SCHEME | Self-declaration by scheme owner See Note 1 | ||||||
| Or | Evaluation of scheme suitability by a recognised authority See Note 2 | ||||||
| Or | Government-owned scheme or government-mandated scheme See Note 3 | ||||||
| Or | Benchmarking of scheme See Note 4 | ||||||
| + | |||||||
CONFORMITY | Scheme owner recognition of other parties assessing against the scheme standards | Scheme owner directly conducting conformity assessment activities | Independent peer assessment for accredited CAB | Peer assessment process managed by government | Accreditation of CAB under global multilateral recognition arrangement by a body peer-evaluated to ISO/IEC 17011 | Government mandate for conformity assessment activity | Benchmarking of scheme by an organization approved to UNIDO benchmarking principles and process |
| = | |||||||
RESULT: | Scheme-derived assurance: Recognition of CAB by registered scheme | Scheme-derived assurance: Self-declaration by registered scheme | Authority-derived assurance: Peer assessment body recognition for accredited CAB | Authority-derived assurance: Recognition by a governmental peer assessment authority | Authority-derived assurance: Global accreditation multilateral recognition arrangement | Authority-derived assurance: Recognition by government mandate | Authority-derived assurance: Recognition by approved benchmarking organisation |
Notes to Table:
- The form of the self-declaration MUST be in accordance with a UNTP template reflecting relevant international standards.
- This refers to evaluation of a scheme by the Global Accreditation Cooperation Incorporated or through this body’s regional accreditation cooperation members or member bodies of its Multilateral Recognition Arrangement for such scope - this supersedes the role of the former International Accreditation Forum (refer www.global-aci.org).
- Ownership or mandate provided by national government or intergovernmental entity.
- Scheme benchmarking organisations ensure that a scheme suitability assessment has been conducted for the candidate scheme.
- A CAB issuing UNTP conformity credentials is sometimes also the scheme owner.
- The linked scheme self-declaration is available to assist in judging credibility of the scheme.
- Users of conformity credentials issued by a CAB recognised under a scheme have the linked scheme self-declaration available containting details of the CAB-approval process used by the scheme owner.
- This pathway applies to CABs accredited under the Multilateral Recognition Arrangement of the Global Accreditation Cooperation Incorporated
- Schemes used by CABs MAY be owned by the peer assessment body but the CAB itself SHALL NOTE be owned by or otherwise related to the peer assessment body.
- Scheme evaluation is a prerequisite for accreditation of CABs by bodies that are signatories to the Global Accreditation Cooperation Incorporated Multilateral Recognition Arrangement.
- UNIDO Global Best Practice Framework for Organisations Performing Benchmarking Activities for Certification-related Conformity Assessment Schemes 2026. The process for approval of benchmarking organisations to the UNIDO principles is still to be defined.
Scheme-declaration process areas, and example international standards for each, are defined on the Conformity Vocabulary Catalog page: see Scheme Declaration and International Standards.
The Components of a Conformity Credential
This section provides illustrative JSON-LD snippets for each Conformity Credential component. For a complete worked example, see the cathode sample credential.
Credential Envelope
All Conformity Credentials are issued as W3C Verifiable Credentials (VCDM 2.0). The credential type includes both VerifiableCredential and DigitalConformityCredential, and the @context references both the W3C VCDM and UNTP context URIs. The issuer id SHOULD be a DID using a supported DID method, with issuerAlsoKnownAs linking to authoritative business register identifiers. The issuing party should be the conformity assessment body (CAB). Please refer to DPP VC Guidance for further information about the use of the verifiable credentials data model for UNTP.
{
  "type": ["DigitalConformityCredential", "VerifiableCredential"],
  "@context": [
    "https://www.w3.org/ns/credentials/v2",
    "https://vocabulary.uncefact.org/untp/0.8.0/context/"
  ],
  "id": "https://credentials.sample-cab.example.com/dcc/mine-001",
  "issuer": {
    "type": ["CredentialIssuer"],
    "id": "did:web:sample-cab.example.com",
    "name": "Sample Conformity Assessment Body",
    "issuerAlsoKnownAs": [
      {
        "id": "https://sample-register.example.com/companies/CAB-001",
        "name": "Sample Conformity Assessment Services Pty Ltd",
        "registeredId": "CAB-001",
        "idScheme": {
          "id": "https://sample-register.example.com",
          "name": "Swiss Central Business Name Index (ZEFIX)"
        }
      }
    ]
  },
  "validFrom": "2025-01-15T00:00:00Z",
  "validUntil": "2028-01-15T00:00:00Z",
  "name": "SCSA Certification — Sample Copper Mine",
  "credentialSubject": { "type": ["ConformityAttestation"], "...": "..." }
}
Validity of the Conformity Credential is managed exclusively through the verifiable credential (VC) envelope that wraps the data set. The principal use case addressed by UNTP is whether a conformity attestation is current now; this is systematically achieved through the VC via revocation status and (where applicable) the validUntil field. The issue date of the VC need not be the same as the date the wrapped certificate was created, but capturing that extra date solves little compared with the wider challenge of out-of-cycle status changes and the implications of preserving a certificate's full revision history over time. The attestation wrapped inside the VC is immutable, so in most scenarios a status change will warrant issuance of a new credential. Preserving full revision history can be solved with VCs — unlike in the paper world — but requires digital machinery that UNTP has opted not to roll out at this early iteration. It is a priority item on the roadmap for future UNTP development, and will most likely remain optional for implementers when available.
Conformity Attestation
The ConformityAttestation is the credentialSubject of the Conformity Credential. It is best thought of as the digital version of the paper product or facility conformity certificate.
- The
idMUST be a globally unique identifier (URI) for the attestation. Typically a certificate number with the CAB web domain as a prefix. assessorLevelclassifies the impartiality of the issuer in relation to the object of assessment, aligned with ISO/IEC 17000:2020 (first-party,second-party,third-party,unspecified).assessmentLevelclassifies the nominated assurance pathway (authority-derived,scheme-derived,unspecified); the detail is carried byauthorityEndorsement,schemeDeclarationorlicensedByScheme.evidenceSelectionstates who selected and supplied the evidence the attestation rests on (self-declared,cab-controlled,independent-source,mixed-source). This is a separate question fromassessorLevel: a third-party assessor may still be working from evidence the assessed party chose.attestationTypeindicates the type of the attestation. It has a broader intent than the ISO/IEC 17000 term attestation: alongsidecertificationanddeclarationit also covers conformity assessment activities that contribute to conformity assessment without necessarily producing a statement of conformity —audit,peer,inspection,testing,verification,validationandcalibration(each defined against an ISO/IEC 17000:2020 or JCGM 200:2012 clause in the code list).issuedToPartyidentifies the entity to whom the attestation is issued — usually the product manufacturer or facility operator.coveragestates what the attestation is designed to cover: the scheme it is issued under, the standards or regulations it serves, and the jurisdictions it is intended to be relied on in. It carries no outcome - see Attestation coverage.authorityEndorsementlists the authority endorsements (for example an accreditation or a government mandate) under which the attestation is issued, where authority-derived assurance is claimed.licensedBySchemeandschemeDeclarationcarry the scheme-derived pathway instead.conformityCertificatelinks to the full certificate document (e.g. a PDF), with optional integrity verification viadigestMultibase.auditableEvidencelinks to the evidence files that informed the assessments. These are usually commercially sensitive but important for audits.conformityAssessmentis an array of detailed assessments made about identified products or facilities against specific criteria.
"credentialSubject": {
  "type": ["ConformityAttestation"],
  "id": "https://sample-scsa-cab.example.com/attestation/SCSA-KM-2025-001",
  "name": "SCSA Responsible Production Certificate — Sample Mine",
  "description": "Third-party conformity assessment of Sample Copper Mine against SCSA Responsible Copper Assessment (RCA) v1.0, covering environmental, social, and governance criteria for responsible copper production.",
  "assessorLevel": "third-party",
  "assessmentLevel": "authority-derived",
  "evidenceSelection": "cab-controlled",
  "attestationType": "certification",
  "issuedToParty": {
    "id": "did:web:sample-mine.example.com",
    "name": "Sample Copper Mine Pty Ltd",
    "registeredId": "MINE-001",
    "idScheme": {
      "id": "https://sample-register.example.com",
      "name": "Patents and Companies Registration Agency (Zambia)"
    }
  },
  "authorityEndorsement": ["..."],
  "coverage": [{"..."}],
  "conformityCertificate": {"..."},
  "auditableEvidence": {"..."},
  "conformityAssessment": ["..."]
}
Authority Endorsement
An AuthorityEndorsement is an authority-derived recognition (for example accreditation under a global multilateral recognition arrangement, or a government mandate) issued to the conformity assessment body, asserted where the attestation claims authority-derived assurance. It provides trust that the CAB is properly recognised to issue attestations under the referenced scheme. Scheme-owner recognition is not an authority endorsement — that is the scheme-derived pathway, carried by licensedByScheme and schemeDeclaration.
endorsementTypeis a code for the type of authority-derived assurance (for exampleauthority-globalmra,authority-mandate,authority-benchmark).namedescribes the accreditation.trustmarkis a base64-encoded image typically shown on paper accreditations.grantingAuthorityidentifies the competent authority that granted the recognition.authorityEvidenceis aLinkto the actual accreditation details. This SHOULD point to a trusted source such as a web page on the accreditation authority site or a digital verifiable credential.
Note that the authorityEndorsement structure is part of the attestation issued by the CAB. As such it is only an unverified claim until confirmed via the authorityEvidence link.
"authorityEndorsement": [
  {
    "endorsementType": "authority-globalmra",
    "name": "Accreditation of Sample Conformity Assessment Body as a certification body under the Global Accreditation Cooperation multilateral recognition arrangement.",
    "trustmark": {
      "name": "SNAB-Accredited Certification Body",
      "description": "Trust mark issued by the Sample National Accreditation Body to accredited certification bodies.",
      "imageData": "c25hYi1sb2dv",
      "mediaType": "image/png"
    },
    "grantingAuthority": {
      "id": "https://sample-snab.example.org",
      "name": "Sample National Accreditation Body",
      "registeredId": "SNAB-AUTH-001",
      "idScheme": {
        "id": "https://sample-snab.example.org",
        "name": "SNAB Registry"
      }
    },
    "authorityEvidence": {
      "linkURL": "https://sample-snab.example.org/accredited-bodies/sample-cab",
      "linkName": "Sample CAB SNAB Accreditation",
      "mediaType": "text/html",
      "linkType": "https://test.uncefact.org/vocabulary/link-type/dcc"
    }
  }
]
Attestation coverage
coverage is an optional array stating what the attestation is designed to cover. Each entry carries a resolvable id, a human-readable name, and an optional coverageType from the attestation-coverage-type code list: scheme, standard, regulation, jurisdictionRecognition or jurisdictionAssessed.
The two jurisdiction values are separate because they answer different questions. jurisdictionRecognition is the jurisdiction in which the attestation is intended to have recognition, acceptance, or legal effect. jurisdictionAssessed is the jurisdiction in which the activities subject to the attestation are conducted by the assessed organisation. An attestation often needs to state both and the two can differ: a certificate issued in one jurisdiction may be designed to be relied on in another.
"coverage": [
  {
    "type": ["AttestationCoverage"],
    "coverageType": "scheme",
    "id": "https://steelcertification.com/schemes/structural-steel/v2026",
    "name": "ACRS Structural Steel Certification Scheme"
  },
  {
    "type": ["AttestationCoverage"],
    "coverageType": "standard",
    "id": "https://store.standards.org.au/product/as-nzs-3679-1-2016",
    "name": "AS/NZS 3679.1:2016 Structural steel - Hot-rolled bars and sections"
  },
  {
    "type": ["AttestationCoverage"],
    "coverageType": "jurisdictionAssessed",
    "id": "https://vocabulary.uncefact.org/country/AU",
    "name": "Australia"
  },
  {
    "type": ["AttestationCoverage"],
    "coverageType": "jurisdictionRecognition",
    "id": "https://vocabulary.uncefact.org/country/NZ",
    "name": "New Zealand"
  }
]
Coverage carries no conformance outcome, it indicates what the attestation applies to at a high level (eg, the name of a scheme or a regulation). The conformance details applicable to the stated attestation coverage are exclusively found within the conformityAssessment entries. This division ensures the conformityAssessment data set represents the sole record of conformance outcomes and the detail for these assessments can restrict the valid applications of the attestation coverage, rather than the other way round.
Conformity Certificate and Auditable Evidence
The conformityCertificate and auditableEvidence properties are both Link objects. The certificate links to the full version of the conformity attestation (e.g. a PDF or web page); the auditable evidence links to the underlying evidence files that informed the assessments.
linkURLpoints to the external resource.linkNameprovides a human-readable description.mediaTypespecifies the content type of the linked resource.linkTypeclassifies the link using a controlled vocabulary.digestMultibasemay optionally be included to ensure content integrity — the hash of the target content at the time the credential was issued.
"conformityCertificate": {
  "linkURL": "https://sample-scsa.example.org/participants/kansanshi-mining",
  "linkName": "SCSA Public Certificate — Sample Copper Mine Pty Ltd",
  "mediaType": "text/html",
  "linkType": "https://test.uncefact.org/vocabulary/link-type/dcc"
},
"auditableEvidence": {
  "linkURL": "https://sample-scsa-cab.example.com/reports/SCSA-KM-2025-001-full.pdf",
  "linkName": "Full Assessment Report — Sample Mine (Restricted)",
  "mediaType": "application/pdf",
  "linkType": "https://test.uncefact.org/vocabulary/link-type/dcc"
}
Conformity Assessment
One Conformity Credential may include many assessments in the conformityAssessment array. Each assessment represents the evaluation of an identified product, facility, or organisation against one or more specific criteria. A single assessment includes:
- A unique
idand human-readablenameanddescription. assessmentCriteria— one or more criteria from a scheme, standard, regulation or other published document, each qualified by acriteriaTypeand classified by aconformityTopic.assessmentDate— OPTIONAL. The date on which the assessment was made. Omit where an assessment is made up of several aspects conducted at different times and no single date captures the whole;assessedPeriodmay still be used to carry the span the records cover.assessedPeriod— OPTIONAL. The period of records the assessment drew on, where it covered a span of time rather than a point in time.assessedPerformance— the outcome of the assessment: a measure, score, determination, or qualitative finding (see Assessed Performance).assessedFacility,assessedProduct, orassessedOrganisation— the subject of the assessment, withidVerifiedByCABindicating whether the CAB verified the subject’s identity.
The assessedPeriod is not the period the credential is valid for. A certificate issued in January 2025 and valid until 2028 may rest on emissions data for the 2024 calendar year, and a reader needs both dates to judge how current the finding is. It sits on the assessment rather than on the attestation because one attestation can carry assessments drawn from different windows: a multi-site certification may assess one facility against records to July and another against records to September.
"conformityAssessment": [
  {
    "type": ["ConformityAssessment"],
    "id": "https://sample-scsa-cab.example.com/assessment/SCSA-KM-2025-001-GHG",
    "name": "GHG Emissions Assessment (Criteria 26, 27)",
    "description": "Assessment of greenhouse gas emissions management, measurement, and reduction initiatives at Sample Copper Mine against SCSA criteria 26 and 27.",
    "assessmentCriteria": ["..."],
    "assessmentDate": "2025-01-10",
    "assessedPeriod": { "startDate": "2024-01-01", "endDate": "2024-12-31" },
    "assessedPerformance": ["..."],
    "assessedFacility": [
      {
        "facility": {
          "id": "https://facility-register.example.com/fac-001",
          "name": "Sample Copper Mine",
          "registeredId": "fac-001"
        },
        "idVerifiedByCAB": true
      }
    ],
    "assessedOrganisation": {
      "type": ["Party"],
      "id": "did:web:sample-mine.example.com",
      "name": "Sample Copper Mine Pty Ltd",
      "registeredId": "MINE-001"
    }
  }
]
Assessment Criteria and Conformity Topic
Each assessment references one or more criteria via the assessmentCriteria array. A criterion identifies a specific auditable requirement, and MUST be classified by a conformityTopic drawn from the UNTP Conformity Topics taxonomy. The criterion id SHOULD be a URI published by the owner of the criteria, for a scheme via the Conformity Vocabulary Catalog, so that the same criterion can be referenced unambiguously across Conformity Credentials, Product Passports and Facility Records.
A criterion is not always drawn from a registered scheme, so criteriaType states what the reference points at: a scheme-criterion, a scheme-profile where a whole profile is referenced rather than a single criterion, a published-standard, a regulation, or an other-published-document such as a journal article, a proprietary specification or an in-house method.
requiredPerformance optionally carries the threshold the criterion requires. A criterion drawn from a published scheme vocabulary already carries its threshold there, so populate it where the scheme or standard owner has not published a fine-grained vocabulary.
"assessmentCriteria": [
  {
    "criteriaType": "scheme-criterion",
    "id": "https://sample-scsa.example.org/rca/v1.0/criterion/26",
    "name": "GHG Emissions — SCSA Criterion 26",
    "conformityTopic": [
      {
        "type": ["ConformityTopic"],
        "id": "https://test.uncefact.org/vocabulary/conformity-topics/greenhouse-gas-emissions",
        "name": "Greenhouse Gas Emissions",
        "definition": "Assessment of direct and indirect greenhouse gas emissions across scopes 1, 2, and 3, including measurement, reporting, and reduction targets aligned with climate science."
      }
    ]
  },
  {
    "criteriaType": "scheme-criterion",
    "id": "https://sample-scsa.example.org/rca/v1.0/criterion/27",
    "name": "Energy Use and Efficiency — SCSA Criterion 27",
    "conformityTopic": [
      {
        "type": ["ConformityTopic"],
        "id": "https://test.uncefact.org/vocabulary/conformity-topics/renewable-energy-use",
        "name": "Renewable Energy Use",
        "definition": "Adoption and integration of renewable energy sources to reduce reliance on fossil fuels and lower the carbon footprint of operations and products."
      }
    ]
  }
]
Assessed Performance
The assessedPerformance array carries the outcome of the assessment. Each entry may reference a metric from the UNTP Performance Metrics taxonomy, and states the result in whichever of four ways fits what was assessed:
| Property | What it carries | Example |
|---|---|---|
measure | A numeric quantity with a unit and optional tolerance | 100 MPa, below 0.01 ppm |
score | A value from a scale the scheme defines | 87/100, AA, Gold |
determination | A conformity outcome from the UN/CEFACT conformity-determination code list | pass, fail, conditional, indeterminate |
qualitativeFinding | The outcome in words, where it does not reduce to any of the above | No dangerous chemicals found |
Any one of these is enough and they may be combined, so an assessment can report both a measured value and the determination that followed from it. assessedPerformance itself remains mandatory: an assessment that states no outcome has not assessed anything. Where a measure is given, the metric that classifies it is required.
A determination of pass is what earlier drafts carried as a boolean conformance on the assessment. It moved onto the performance entry so that an assessment testing several metrics can report an outcome per metric, and so that a score is not asked to carry outcomes that are not scores.
Performance is shared with the self-declared claims in a product passport and a facility record, so the same four properties appear there. What they mean does not change, but who is asserting them does. On an assessedPerformance in a conformity credential, a determination is an independent finding by the conformity assessment body named as the issuer, reached under the assessorLevel, assessmentLevel and evidenceSelection the attestation declares. On a self-declared claimedPerformance, the same value is the issuer's own judgement about its own product or facility. A verifier should weigh the two differently, and the distinction is carried by which credential the outcome sits in rather than by the property name.
"assessedPerformance": [
  {
    "metric": {
      "id": "https://vocabulary.uncefact.org/performance-metrics/scope-1-ghg-emissions",
      "name": "Scope 1 GHG Emissions"
    },
    "measure": {
      "value": 45000,
      "unit": "TNE"
    }
  }
]